Multi-tenant SharePoint and OneDrive policy management for MSPs

Audit SharePoint and OneDrive sharing across every client tenant against a security baseline, fix loose settings in bulk, and get told when a client drifts.
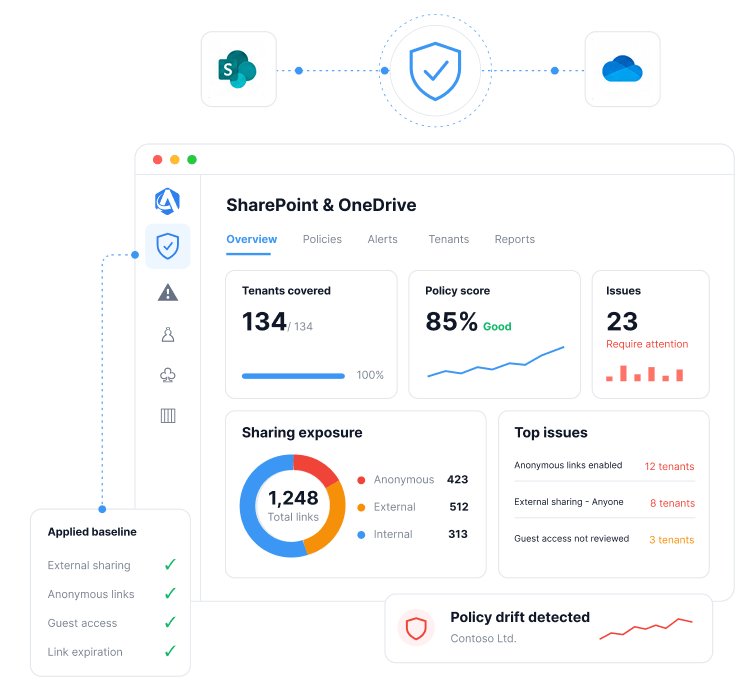
Web page analyze 1
Audit

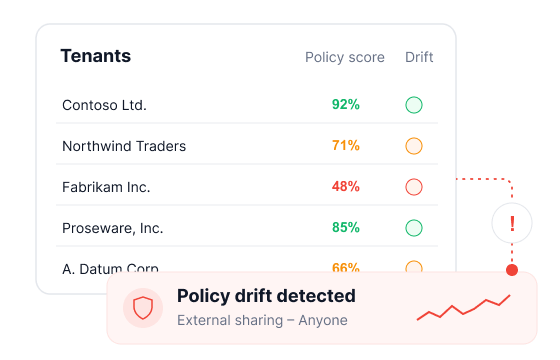
Every tenant scored against a baseline

Mouse cursor add
Remediate

Fix a loose setting in a click, in the real tenant

radar ai
Monitor

Drift alerts when a control moves off the standard

Chart
Report

Exportable evidence mapped to recognized standards
Why managing SharePoint and OneDrive tenant by tenant stops working at scale
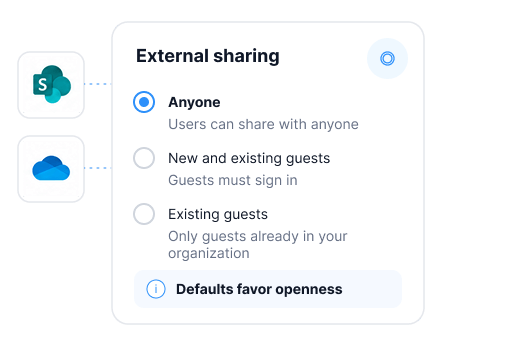
Defaults favor ease of use

SharePoint and OneDrive ship tuned for collaboration, not containment. Easy to work in on day one, and an easy target until somebody tightens it.

One admin center per client

The SharePoint admin center is single-tenant. Across every client an MSP manages it is the same configuration work repeated per client, or a script somebody now owns and maintains.

Drift goes unnoticed

A setting loosened for one project stays loosened, and nothing surfaces it. Without a cross-tenant view, nobody can say which clients are still configured correctly.
Know exactly which clients are sharing too openly, and close it today
Cross-tenant sharing audit against a security baseline

Every managed tenant is scored against the same baseline on one screen. External sharing scope, default link behavior, expiration and resharing are all read from the real tenant.

Remediate in bulk, across every tenant

Controls, settings and sharing policies are fixed from Augmentt and pushed to every tenant that needs them at once, baselining the whole client base onto the same posture. No admin center per client, no script to maintain.

Approved-domain and security-group allowlists

External collaboration is rarely all-or-nothing. Manage the domains a client may share with, and the security groups permitted to share out, alongside the sharing controls.

Drift detection on the controls that matter

When a control drifts off the baseline, Augmentt flags it against the same benchmark the audit uses, with the alerting, auto-remediation and snoozing already in the platform.
One source for the fix and the evidence

Every action a team takes in SharePoint and OneDrive maps back to a recognized standard. Export the evidence in a click when an auditor or a cyber insurer asks for it, instead of rebuilding it by hand. And when a control needs premium Microsoft licensing, the view says so, turning a compliance gap into a licensing upsell.

CIS Microsoft 365
HIPAA
CMMC
NIST CSF
Essential Eight
SOC 2
Native admin centers vs. Augmentt

The same five jobs, done per tenant or done once.

The job
See sharing posture across clients
Fix a permissive setting
Notice when it changes
Standardize a new client
Prove it to a client or auditor
SharePoint admin center + scripts
One login per tenant, one screen at a time
Manual change per tenant, or PowerShell somebody maintains
Nothing tells you; it surfaces in the next audit
Rebuild the same settings by hand, or fork a script per tenant
Screenshots assembled by hand before the QBR
Every managed tenant in one view, scored against your benchmark
One-click remediation, applied in the real tenant
Posture drift alerts, with auto-remediation and snoozing
Save a policy template once and push it to every tenant, so every client starts from the same baseline
Exportable posture reporting mapped to recognized standards
Three steps to managing SharePoint and OneDrive policy at scale

01

Connect the tenants

Magic Link onboarding and GDAP automation bring client tenants in on the permission model an MSP already uses for Conditional Access and Intune.

02

Audit against the benchmark

See how each tenant’s SharePoint and OneDrive sharing controls score against your preferred benchmark, and where licensing limits what a client can enforce.

03

Remediate and hold it

Fix loose controls from Augmentt, keep allowlists current, and let drift alerts tell the team when a tenant moves off the standard.

What changes for your team

The same coverage pays off differently depending on which seat you sit in.

A billable service instead of an absorbed project
One screen instead of one admin center per client

"We built an entire managed service around the Augmentt platform so we can sell our customers a service that will keep their tenants up to date and configured all the time rather than needing to do these professional services engagements periodically."

Tim Campbell
Practice Director, All Covered
SharePoint & OneDrive management FAQs

Common questions from MSPs evaluating multi-tenant SharePoint and OneDrive policy management.

What is multi-tenant SharePoint and OneDrive policy management?

It is managing SharePoint Online and OneDrive tenant-level settings across many Microsoft 365 tenants from one console instead of opening the SharePoint admin center for each client. Augmentt audits those controls against the CIS Microsoft 365 Benchmark on every managed tenant, remediates from one place, and flags a tenant when it drifts.

The tenant-level sharing and access controls in the SharePoint and OneDrive section of the CIS Microsoft 365 Benchmark — external sharing scope, default link behavior and link expiration, external resharing, and which security groups may share externally — plus approved-domain and security-group allowlists managed inside Augmentt. Coverage is shown control by control in the compliance view.

For the controls Augmentt manages, a technician works cross-tenant from Augmentt instead of opening the admin center per client. Augmentt edits the real policy in the real tenant, so the setting is where Microsoft expects to find it.
A law firm and a marketing agency have genuinely different collaboration needs. Augmentt reads and manages each tenant individually rather than pushing from a master tenant, so tenants can hold different postures while every one of them is measured against the same benchmark.
Drift on a managed control is flagged against the same benchmark the audit uses, and the platform’s alerting, auto-remediation and snoozing apply — so a loosened sharing setting surfaces as an alert rather than as an audit finding later.
Augmentt focuses on tenant-level policy, which governs sharing behavior for every SharePoint site and OneDrive account in the environment and is where cross-tenant standardization work sits for an MSP.
Relevant Microsoft licensing requirements are surfaced in the compliance view, so the gap is visible per tenant and becomes a concrete licensing conversation rather than a surprise.
Every check maps to a recognized standard — CIS, HIPAA, CMMC, NIST CSF and Essential Eight — and posture is exportable. Augmentt evidences control state, so the report a client sees and the evidence an auditor sees come from the same source.
Lighthouse is oriented to identity and threat protection and does not reach SharePoint, OneDrive, Purview or Teams policy. That is why MSPs have had no cross-tenant answer for data and collaboration settings.
Yes. SharePoint and OneDrive sit alongside Conditional Access, Microsoft Intune, Defender, Purview DLP and sensitivity labels, and Microsoft Teams policy in the same multi-tenant console, with one compliance view across all of them.

See where every client's sharing posture actually stands

Run Microsoft 365 security reports across your customers and see the SharePoint and OneDrive controls that are open today.

HIPAA
Healthcare & BAAs
MAPPED

NIST / CIS

Safety standards

MAPPED

CMMC

Federal contracting & DoD
MAPPED